Autenix Compliance
Continuous compliance across 35+ frameworks. One platform for every control, every framework, every audit. Six modules built in — from continuous monitoring to vendor risk.
- Risk ManagementProactive risk assessment that drives smarter decisions
- Trust CenterProve your security posture before prospects ask
- Audit ReadinessBe audit-ready every day, not just audit week
- Policy GeneratorProfessional policies in minutes, not months
- Vendor Risk ManagementManage third-party risk at scale
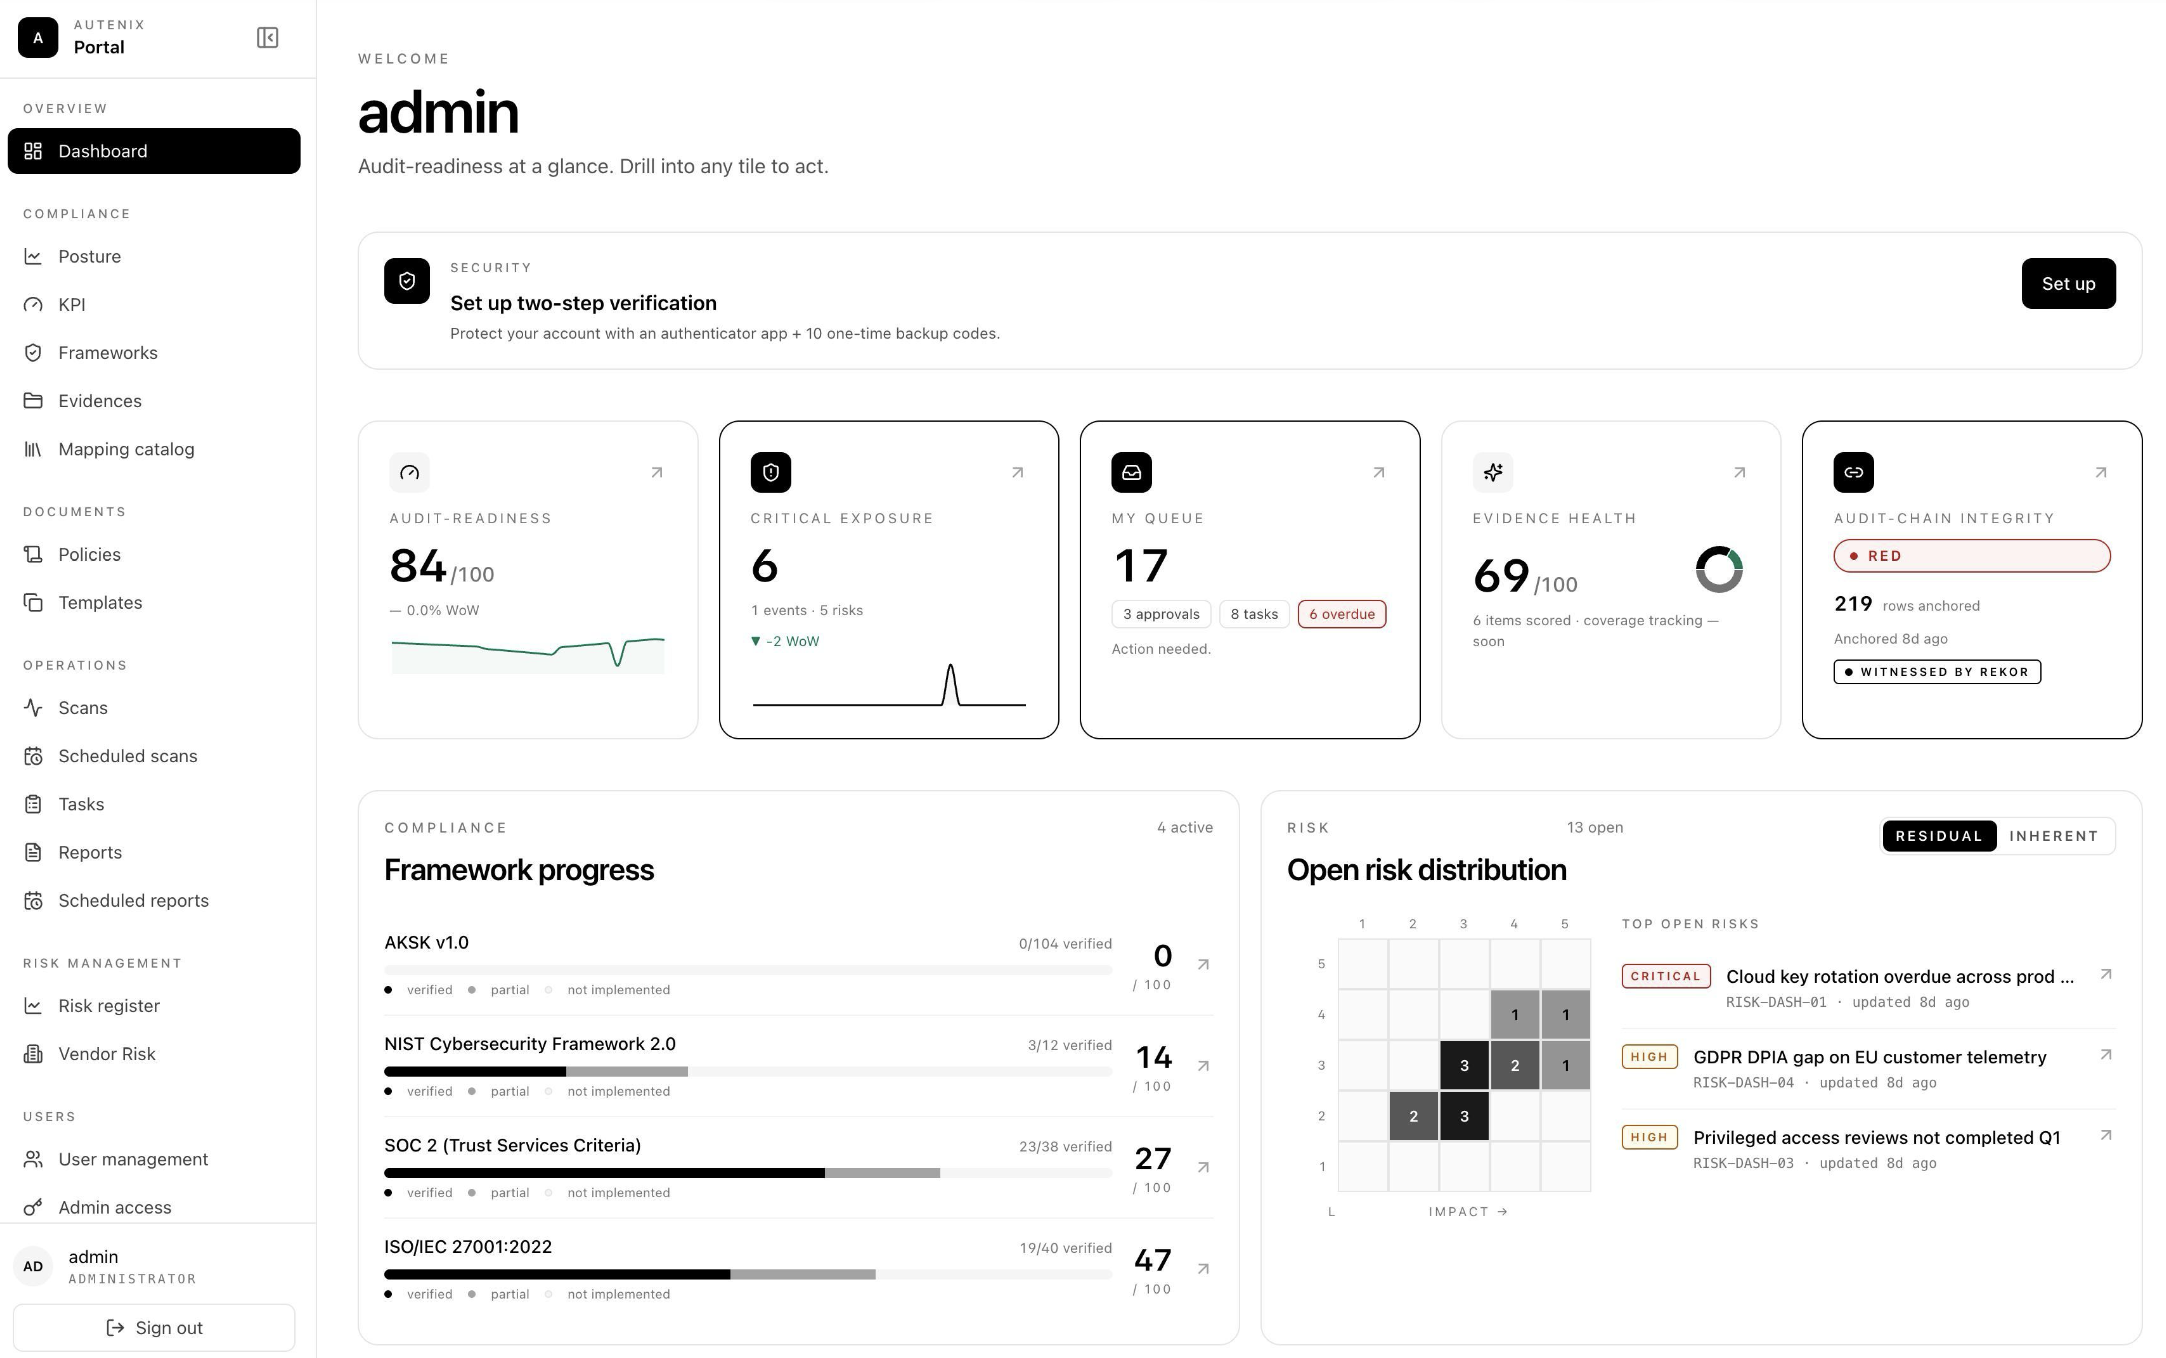
Audit readiness, framework progress, and open risk — the Compliance dashboard.
How Autenix Compliance works
Four steps from "no framework in place" to "audit-ready every day."
Connect your stack
Plug in AWS, Azure, GCP, Kubernetes, M365, GitHub, and more. No agents.
Map to your frameworks
Autenix maps findings to SOC 2, ISO 27001, HIPAA, PCI-DSS, and 35+ other frameworks automatically.
Collect evidence continuously
Evidence flows in around the clock. No screenshots, no exports, no audit-week panic.
Stay ahead of drift
Real-time alerts the moment a control drifts. Remediate before it becomes an audit finding.
Every compliance module, built in.
Risk, Trust Center, Audit Readiness, Policy Generator, Vendor Risk — all five specialized modules live inside Autenix Compliance.
Compliance for Every Framework
From SOC 2 to ISO 27001, we support the frameworks that matter most to your business and customers.
Autenix Compliance — Frequently Asked Questions
Common questions about SOC 2, ISO 27001, HIPAA, and the Compliance platform.
Ready to be audit-ready every day?
See how Autenix Compliance automates SOC 2, ISO 27001, HIPAA, and 35+ more frameworks — all under one platform.